The SDG Security Portal

Comprehensive protection for your IT systems

We support you in setting up and configuring your personal security portal.
Comprehensive protection for all your systems.

Your Security Portal

A holistic approach to securing IT infrastructures, delivered in cooperation with our partner Enginsight, is vital for protecting business operations and keeping them efficient. A comprehensive assessment of the technological maturity of your IT infrastructure ensures that business processes run smoothly and securely. Efficient vulnerability management means security gaps are analysed precisely and minimised. Proactive recommendations and automated solutions help to significantly reduce the attack surface. In the event of a cyberattack, the system responds autonomously by automatically blocking attackers in order to minimise potential damage. It also supports the set-up and operation of an information management system in line with the high standards of ISO 27001, to ensure optimal information processing.

4 steps towards better IT security
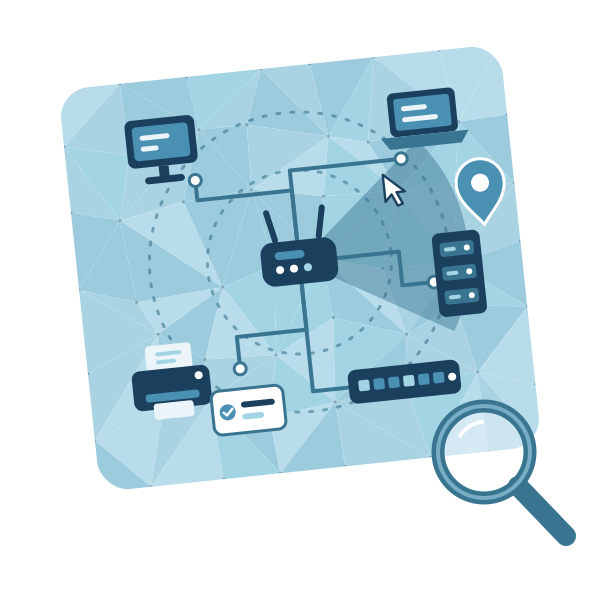
Network diagram with computers, printers and devices under a magnifying glass: inventory

Automatic discovery, IP inventory and classification of all network devices

The comprehensive listing covers Windows, macOS and Linux devices, VM hosts and IP devices such as printers, routers and switches. An interactive map of your IT landscape, visual representations and the documentation of responsibilities provide a clear overview and effective management.

Magnifying glass examining files and systems, with a risk indicator below

Automated and complete security scan of your entire IT in a short time

This innovative security solution ensures 100% detection of vulnerabilities through CVE scans. With effective configuration management, an intuitive security rating (A+ to F), live attack detection and system event log analysis, it provides comprehensive security for servers, clients and the web.

Server with stethoscope and monitor with pulse line: continuous monitoring of systems

Maintaining resilience through health checks or in-depth analyses

The Operation Management Dashboard enables efficient monitoring of processes, services and software. With network monitoring (ping, port, SNMP), integrity monitoring of critical files and automated actions in the event of an alarm, the solution provides comprehensive security. It also allows you to monitor any metrics of your choice (custom metrics) and detects anomalies using machine learning.

Gears with synchronisation arrows, server and smartphone: automated processes

Automatic response to system events and autonomous execution of routine tasks

The solution offers a wide range of automated functions, including the execution of scripts, cron jobs and live scans of the security status. Webhooks, instant messaging and SMS notifications keep you informed at all times. It also enables automatic fixing of server configurations and automatic updates through the update manager.

3 tools for better IT security

Secured gate between laptop and server: controlled access

Hacktor - penetration tests

With this tool, penetration tests are carried out at set intervals on your company's entire infrastructure, on individual websites or on specific IP addresses. Known vulnerabilities and weaknesses (CVEs) are detected in the process. The Hacktor also performs footprinting, recording publicly accessible information about the system. It also checks for configuration weaknesses, for example regarding encryption, authentication and assigned privileges.

Magnifying glass over a network of connected points

Pulsar Agent - the view from the inside

The Pulsar Agent is a highly developed security instrument that penetrates deep into networks to detect vulnerabilities from the inside. Using CVE scanners, it identifies potential points of attack and enables efficient patch management. Precise analysis of network traffic by means of deep packet inspection ensures early detection of threats. The agent also protects the system through dynamic blocking of network attacks via IPS. If required, manual blocking and microsegmentation provide additional layers of security. Suspicious behaviour is identified through anomaly detection using machine learning. Port monitoring, software inventory and further functions make the Pulsar Agent an indispensable tool for comprehensive network security.

Large eye in a network: observation of the attack surface

Observer - the view from the outside

The Observer is an external guardian that monitors the system to be protected from the outside. Using CVE scanners, it detects vulnerabilities and thus enables proactive security measures. The uptime monitor ensures that the availability of the system is monitored continuously. SSL/TLS checks ensure secure data transmission, while DNS monitoring uncovers irregularities at an early stage. Footprinting of the application environment creates a comprehensive understanding of potential attack vectors. Port scans identify open access points, while HTTP header analysis and redirect monitoring provide additional insight into the system architecture. The Observer is therefore an indispensable tool for holistic external security monitoring.

Security Information and Event Management

Security Information and Event Management (SIEM) provides a holistic view of IT security by collecting and analysing messages and log files from different systems. Suspicious events or dangerous trends can be detected in real time.

The integrated cockpit offers a central dashboard with a comprehensive overview of all aspects. The data lake serves as a central repository with targeted filters for efficient data management. With the help of obfuscators, the solution protects sensitive information through authorised users, two-factor authentication and field masking. Workflows capture events and trigger automated routines and alarms. Extractors enable the structured extraction of information from log files and event data, recognise patterns and derive security optimisations. The use of collectors and collector relays optimises resource utilisation for log collection, thus ensuring efficient and comprehensive security monitoring.